preloader

Enterprise Infrastructure as Code
(IaC) Solutions

SNWN Tech Solution delivers Infrastructure as Code (IaC) services to automate provisioning, eliminate configuration drift, and scale cloud infrastructure efficiently. Using Terraform, AWS CDK, and Ansible, we build secure, version-controlled, reproducible environments across physical, virtual, and multi-cloud platforms, improving operational consistency, deployment speed, infrastructure reliability, and enterprise scalability.

01

Version-Controlled Infrastructure

Review and track every infrastructure change.

02

Cloud Provisioning Automation

Build consistent environments with Terraform and related tools.

03

Policy & Drift Management

Apply guardrails and detect configuration changes.

Delivery challenges

The Infrastructure Reality: ClickOps vs. The SNWN IaC Framework

Engineering teams move faster when their delivery process is visible, repeatable, and easy to improve.

Business growth
Fragmented systems
Operational strain
Pressure point 01

Snowflake Environments

Dev, Staging, and Production drift apart over time due to ad-hoc console tweaks and unrecorded modifications.

Operational impact
This makes changes harder to review and repeat across teams.
How SNWN responds
Immutable Parity: Environments are instantiated from the exact same code modules, ensuring 100% parity across all lifecycle stages.
Pressure point 02

Disaster Recovery Speed

Rebuilding compromised or degraded infrastructure takes days of manual configuration and trial-and-error guessing.

Operational impact
The extra handoffs can delay releases and make ownership unclear.
How SNWN responds
Instant Re-Provisioning: Execute an automated pipeline to rebuild the entire enterprise infrastructure stack from scratch within minutes.
Pressure point 03

Security Blind Spots

Accidental misconfigurations (such as exposed storage buckets or open security groups) remain unnoticed until breached.

Operational impact
Teams may spend time fixing avoidable differences between environments.
How SNWN responds
Policy as Code: Infrastructure code is scanned by automated static analyzers (Checkov, OPA) prior to deployment to block security flaws.
Pressure point 04

Cloud Cost Sprawl

Forgotten test servers and unattached volumes run idle indefinitely, wasting significant cloud budget.

Operational impact
Without useful feedback, reliability problems can be harder to catch early.
How SNWN responds
Ephemeral Environments: Spin up isolated environments automatically for feature branch testing and tear them down upon pull request closure.

Engineering capability map

Core IaC Service Capabilities

Connect the right engineering practices, automation, and platform tools to the way your teams deliver software.

DeclareVersioned configuration
ValidateReview and policy checks
ProvisionRepeatable environments
MaintainDrift and change control
Capability 01

Multi-Cloud Provisioning & Architecture

Engineer modular, reusable declarative templates to provision resilient VPCs, databases, and compute infrastructure seamlessly across AWS, Azure, and GCP.

Practical deliverables

  • Engineer modular, reusable declarative templates to provision resilient VPCs, databases, and compute infrastructure seamlessly across AWS, Azure, and GCP.
Capability 02

Configuration Management & Machine Templating

Automate operating system configurations, security baseline hardening, and golden image baking using Ansible, Packer, and Chef across all environments.

Practical deliverables

  • Automate operating system configurations, security baseline hardening, and golden image baking using Ansible, Packer, and Chef across all environments.
Capability 03

Policy-as-Code & Automated Governance

Embed automated compliance and security guardrails directly into provisioning pipelines using Open Policy Agent and Sentinel to prevent misconfigurations.

Practical deliverables

  • Embed automated compliance and security guardrails directly into provisioning pipelines using Open Policy Agent and Sentinel to prevent misconfigurations.
Capability 04

Programmatic IaC & Developer Frameworks

Construct programmatic cloud infrastructure with AWS CDK and Pulumi using TypeScript, Python, or Go backed by automated unit tests.

Practical deliverables

  • Construct programmatic cloud infrastructure with AWS CDK and Pulumi using TypeScript, Python, or Go backed by automated unit tests.
Capability 05

Automated Drift Detection & GitOps Reconciliation

Deploy continuous GitOps reconciliation operators to detect unauthorized runtime drift and automatically restore infrastructure state back to Git baselines.

Practical deliverables

  • Deploy continuous GitOps reconciliation operators to detect unauthorized runtime drift and automatically restore infrastructure state back to Git baselines.

Applied engineering workflows

Practical Enterprise Infrastructure as Code (IaC) Solutions Use Cases

See how platform engineering improvements can reduce friction in the everyday work of building and operating software.
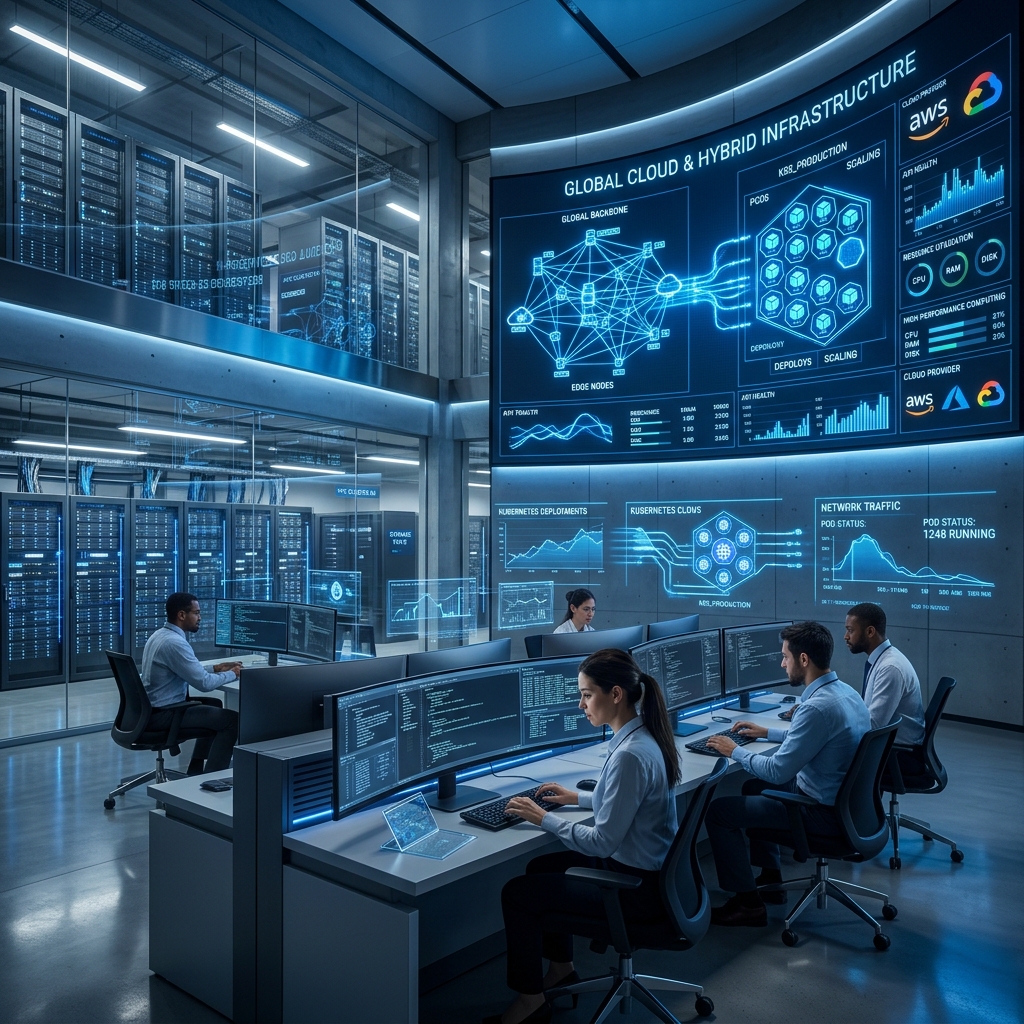
Core Infrastructure as Code Capabilities - SNWN Tech Solution
Built around your sectorEngineering For,
Enterprise Infrastructure as Code (IaC) Solutions

Select a use case to view its scenario, outcome and delivery steps.

Use Case 01

99% Configuration Consistency

Related: DevOps Consulting →

Eliminate snowflake servers, unauthorized console interventions, and configuration drift through declarative IaC templates across multi-cloud enterprise production environments.

OutcomeEliminate snowflake servers, unauthorized console interventions, and configuration drift through declarative IaC templates across multi-cloud enterprise production environments.
  1. Review

    Dev, Staging, and Production drift apart over time due to ad-hoc console tweaks and unrecorded modifications.

  2. Design

    Engineer modular, reusable declarative templates to provision resilient VPCs, databases, and compute infrastructure seamlessly across AWS, Azure, and GCP.

  3. Automate

    Eliminate snowflake servers, unauthorized console interventions, and configuration drift through declarative IaC templates across multi-cloud enterprise production environments.

  4. Improve

    Comprehensive analysis and reverse-engineering of active cloud assets to identify uncodified resources, security risks, and technical debt.

Use Case 02

< 10-Minute Environment Provisioning

Related: CI/CD Automation →

Spin up automated, production-identical environments for testing, staging, and disaster recovery in under ten minutes using modular declarative templates.

OutcomeSpin up automated, production-identical environments for testing, staging, and disaster recovery in under ten minutes using modular declarative templates.
  1. Review

    Rebuilding compromised or degraded infrastructure takes days of manual configuration and trial-and-error guessing.

  2. Design

    Automate operating system configurations, security baseline hardening, and golden image baking using Ansible, Packer, and Chef across all environments.

  3. Automate

    Spin up automated, production-identical environments for testing, staging, and disaster recovery in under ten minutes using modular declarative templates.

  4. Improve

    Design and construction of tailored, highly secure IaC module libraries covering Network topologies, Compute fleets, Storage, and Security policies.

Use Case 03

100% Infrastructure Auditability

Related: Release & Environment Management →

Track every infrastructure modification through peer-reviewed pull requests, automated security scans, and immutable Git version control for total compliance.

OutcomeTrack every infrastructure modification through peer-reviewed pull requests, automated security scans, and immutable Git version control for total compliance.
  1. Review

    Accidental misconfigurations (such as exposed storage buckets or open security groups) remain unnoticed until breached.

  2. Design

    Embed automated compliance and security guardrails directly into provisioning pipelines using Open Policy Agent and Sentinel to prevent misconfigurations.

  3. Automate

    Track every infrastructure modification through peer-reviewed pull requests, automated security scans, and immutable Git version control for total compliance.

  4. Improve

    Import active infrastructure cleanly into state tracking frameworks without service disruption, recreation, or downtime.

Delivery approach

How We Deliver Enterprise Infrastructure as Code (IaC) Solutions Projects

We work in clear stages, validate changes with your team, and prepare the workflow for ongoing ownership.

Select a step to explore its activities, buyer inputs and outputs.

  1. Step 01

    Infrastructure Forensic Audit

    Comprehensive analysis and reverse-engineering of active cloud assets to identify uncodified resources, security risks, and technical debt.

    Engineering Activities

    • Comprehensive analysis and reverse-engineering of active cloud assets to identify uncodified resources, security risks, and technical debt.

    Buyer Inputs

    • Share relevant repositories, environments, access, and team ownership for this stage.

    Concrete Outputs

    • Documented results and agreed next actions for infrastructure forensic audit.
  2. Step 02

    Standardized Module Architecture

    Design and construction of tailored, highly secure IaC module libraries covering Network topologies, Compute fleets, Storage, and Security policies.

    Engineering Activities

    • Design and construction of tailored, highly secure IaC module libraries covering Network topologies, Compute fleets, Storage, and Security policies.

    Buyer Inputs

    • Share relevant repositories, environments, access, and team ownership for this stage.

    Concrete Outputs

    • Documented results and agreed next actions for standardized module architecture.
  3. Step 03

    Zero-Downtime State Migration

    Import active infrastructure cleanly into state tracking frameworks without service disruption, recreation, or downtime.

    Engineering Activities

    • Import active infrastructure cleanly into state tracking frameworks without service disruption, recreation, or downtime.

    Buyer Inputs

    • Share relevant repositories, environments, access, and team ownership for this stage.

    Concrete Outputs

    • Documented results and agreed next actions for zero-downtime state migration.
  4. Step 04

    Continuous Integration & Deployment

    Integration of IaC repositories into CI/CD pipelines configured with automated static analysis, plan generation, and review gates.

    Engineering Activities

    • Integration of IaC repositories into CI/CD pipelines configured with automated static analysis, plan generation, and review gates.

    Buyer Inputs

    • Share relevant repositories, environments, access, and team ownership for this stage.

    Concrete Outputs

    • Documented results and agreed next actions for continuous integration & deployment.
  5. Step 05

    Enablement & Knowledge Handoff

    In-depth enablement workshops, complete documentation, and operational training to empower your internal teams to manage IaC workflows with confidence.

    Engineering Activities

    • In-depth enablement workshops, complete documentation, and operational training to empower your internal teams to manage IaC workflows with confidence.

    Buyer Inputs

    • Share relevant repositories, environments, access, and team ownership for this stage.

    Concrete Outputs

    • Documented results and agreed next actions for enablement & knowledge handoff.

Ownership, guardrails & operations

Build a Platform Teams Can Safely Own

Good engineering workflows make the paved path easy to use while keeping security, reliability, and ownership visible.

Service scope and boundaries

Before delivery starts, we agree which repositories, cloud accounts, clusters, pipelines, and environments are in scope, along with change controls, access needs, and the teams responsible for ongoing operations.

Developer-friendly standards

Make common engineering tasks easier to start and repeat.

  • Modular IaC blueprints enabling rapid enterprise provisioning.
  • Enterprise state management ensuring zero downtime migrations.

Security and reliability guardrails

Build review, access, and policy checks into the workflow.

  • Zero trust security with automated policy guardrails.
  • Automated drift detection reconciling approved Git baselines.

Operational ownership

Keep service owners, support paths, and follow-up work clear.

  • Vendor agnostic orchestration across diverse cloud environments.

Engineering readiness checklist

Enterprise Infrastructure as Code (IaC) Solutions Readiness Checklist

Use these checks to prepare your team, repositories, environments, and delivery goals for a focused engineering review.

Workflow & ownership

4 checks
  • 99.99% Configuration Consistency Guarantee
  • < 10-Minute Rapid Environment Provisioning
  • 100% Infrastructure Auditability via Git Versioning
  • Automated Continuous Drift Detection & Remediation

Automation & environments

4 checks
  • Declarative Provisioning with Terraform & OpenTofu
  • Programmatic IaC with AWS CDK, Pulumi & CDKTF
  • Machine Templating with Ansible, Packer & Chef
  • Automated Policy-as-Code with OPA & Sentinel

Reliability & operations

4 checks
  • Multi-Cloud Architecture (AWS, Azure, GCP)
  • Zero-Downtime State Import & State Locking
  • Ephemeral Environments for Automated Feature Branch Testing
  • 24/7 Platform Engineering Advisory Support

Common questions

Frequently Asked Questions - Enterprise Infrastructure as Code (IaC) Solutions

Clear answers to help your team plan the right next step.

Will implementing Infrastructure as Code modify or disrupt our existing operational workloads?

No. SNWN Tech Solution utilizes targeted import protocols to onboard live resources directly into state management engines without modifying or re-creating them. This establishes code tracking seamlessly while keeping your production services running without interruption.

We operate across multiple cloud providers. Can we manage all environments through a single framework?

Yes. We implement multi-cloud, agnostic solutions like Terraform and OpenTofu. This allows your team to orchestrate AWS, Azure, Google Cloud, and SaaS platforms (such as Datadog, PagerDuty, or Cloudflare) through unified syntax and operational workflows.

What is configuration drift and how does SNWN remediate it?

Configuration drift occurs when ad-hoc manual console changes cause active infrastructure to diverge from documented specifications. We implement automated drift detection and GitOps reconciliation pipelines that alert engineers or automatically restore state to the approved Git baseline.

How does Policy-as-Code prevent security vulnerabilities before deployment?

Policy-as-Code embeds automated static scanning (e.g., Checkov, OPA, Sentinel) directly into your CI/CD pipelines. Every pull request is validated against strict compliance and security rules - blocking unencrypted databases, public buckets, or open ports before they can be applied.
Start a practical conversation

Ready to Automate & Standardize Your Enterprise Infrastructure?

Partner with certified IaC architects and DevOps engineers at SNWN Tech Solution to eliminate configuration drift, automate provisioning, and build resilient multi-cloud foundations.